Wide display typography creates unmistakable presence
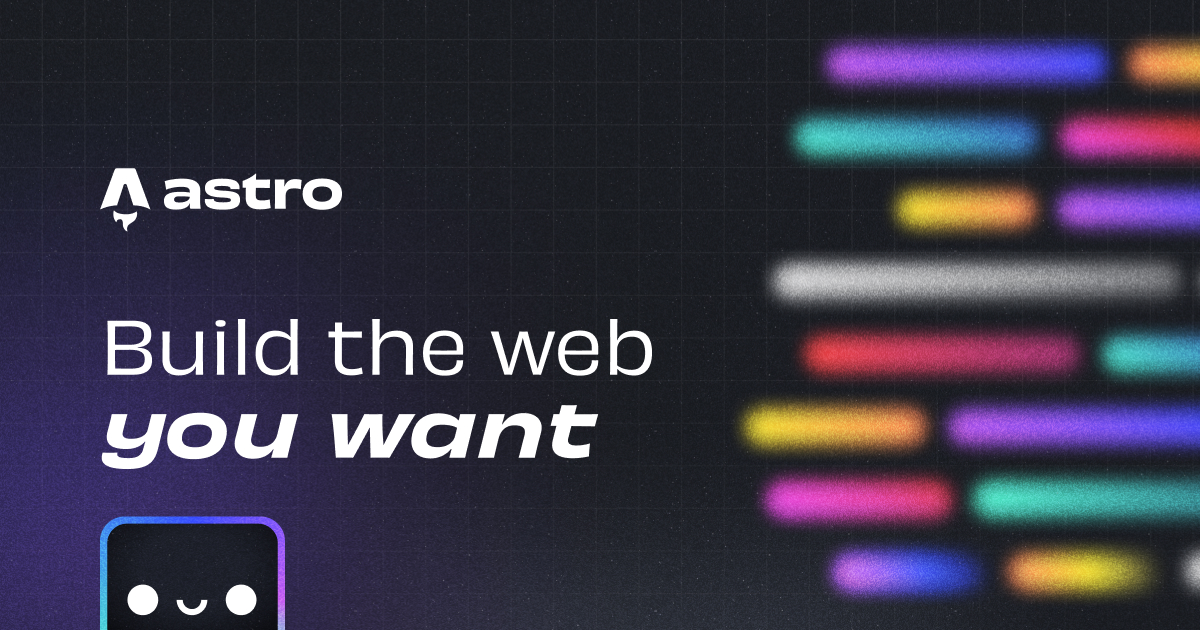
Distinctive wide display lettering immediately sets Astro apart from uniform sans-serif developer pages.
Words
786
Action candidates
15
Links
97/39
HTML
308 KB
astro.build
Astro
Astro builds fast content sites, powerful web applications, dynamic server APIs, and everything in-between.
Distinctive wide display lettering immediately sets Astro apart from uniform sans-serif developer pages.
Showing React, Vue, Preact, and Svelte controls upfront removes adoption hesitation.
Response headers omit Strict-Transport-Security and several graphic elements lack alt attributes.
Add Strict-Transport-Security at the edge CDN and set accurate or empty alt attributes on icons.
ABCDEFGHIJKLMNOPQRSTUVWXYZ · 0123456789
Deep cosmic navy, wide display type, and violet nebula light frame content-first performance with bold energy.
TYPE SCALE
48px / 16px
3.00× display ratio
RHYTHM
LH 24px
Wt 700 · Track normal
CORNERS
/* Extracted design tokens from astro.build via VibeCheck */
:root {
  --color-bg: #060913;
  --color-surface: #1c146c;
  --color-ink: #f2f6fa;
  --color-accent: #5818a8;
  --color-muted: #4c1484;
  --font-display: "Obviously", system-ui, -apple-system, "PingFang SC", "Noto Sans SC", sans-serif;
  --font-body: "Apple Color Emoji", system-ui, -apple-system, "PingFang SC", "Noto Sans SC", sans-serif;
  --text-h1: 48px;
  --text-body: 16px;
  --leading-body: 24px;
  --tracking-display: normal;
  --radius-button: 9999px;
  --space-section: 0px;
  --shadow-surface: rgba(0, 0, 0, 0) 0px 0px 0px 0px, rgba(0, 0, 0, 0) 0px 0px 0px 0px, rgba(0, 0, 0, 0.1) 0px 1px 3px 0px, rgba(0, 0, 0, 0.1) 0px 1px 2px -1px;

  /* Source custom properties sample */
  --ec-brdWd: 1.5px;
  --ec-gtrFg: #686c76;
  --ec-brdCol: rgb(84 88 100);
  --ec-brdRad: 0.375rem;
  --ec-codeBg: #17191e;
  --ec-codeFg: #eef0f9;
  --mono-calt: "calt" on;
  --mono-ital: "ital" 0;
}
Parameters are element samples. Empty values are unknown, and individual samples are not site-wide rules.
Response headers omit Strict-Transport-Security and several graphic elements lack alt attributes.
→ Add Strict-Transport-Security at the edge CDN and set accurate or empty alt attributes on icons.
headers missing HSTS; subset of img missing altWithout Strict-Transport-Security, a first visit can still be downgraded to http. Browsers will not pin HTTPS.
→ Set Strict-Transport-Security: max-age=31536000; includeSubDomains at the edge.
strict-transport-security missingA CSP is the standard way to limit script sources. Vibe-coded pages often load anything, including injected scripts.
→ Start with a report-only CSP, then default-src 'self' and an explicit script-src.
content-security-policy missingWithout nosniff, browsers may interpret a file as a different type than you sent. It is a one-line header.
→ Set X-Content-Type-Options: nosniff.
x-content-type-options missingThe default referrer can leak internal paths and query strings to third parties.
→ Set Referrer-Policy: strict-origin-when-cross-origin.
referrer-policy missingSwitch between page fixes, style recreation, DESIGN.md, or a reusable SKILL.md guardrail file.
Improve the current project using the 2026-11-11T09:07:45.294Z snapshot of https://astro.build. First identify changes since capture; do not revert newer behavior to the old snapshot.

Design baseline
Stack a release badge, wide display headline, and Get Started CTA above interactive framework tabs and Islands diagrams.
{
  "colors": [
    {
      "role": "bg",
      "hex": "#060913"
    },
    {
      "role": "surface",
      "hex": "#1c146c"
    },
    {
      "role": "ink",
      "hex": "#f2f6fa"
    },
    {
      "role": "accent",
      "hex": "#5818a8"
    },
    {
      "role": "muted",
      "hex": "#4c1484"
    }
  ],
  "fonts": {
    "body": "Apple Color Emoji",
    "display": "Obviously",
    "stack": [
      "ui-sans-serif",
      "Obviously",
      "Inter",
      "ui-monospace"
    ]
  },
  "radius": {
    "button": "9999px",
    "card": "",
    "field": ""
  },
  "space": {
    "section": "0px",
    "card": ""
  },
  "type": {
    "h1": "48px",
    "body": "16px",
    "weight": "700",
    "lineHeight": "24px",
    "letterSpacing": "normal"
  }
}
Values come from one capture. Fonts, radii and spacing are element samples, not a universal site-wide specification. Empty values are unknown. HTML bytes are source size, not compressed transfer size; script counts are DOM tags, not network requests.

Actions
1. Enable HSTS and complete alt text on decorative graphics
Add Strict-Transport-Security at the edge CDN and set accurate or empty alt attributes on icons.
Evidence: headers missing HSTS; subset of img missing alt

2. No HSTS header
Set Strict-Transport-Security: max-age=31536000; includeSubDomains at the edge.
Evidence: strict-transport-security missing

3. No Content-Security-Policy
Start with a report-only CSP, then default-src 'self' and an explicit script-src.
Evidence: content-security-policy missing

4. No X-Content-Type-Options
Set X-Content-Type-Options: nosniff.
Evidence: x-content-type-options missing

5. No Referrer-Policy
Set Referrer-Policy: strict-origin-when-cross-origin.
Evidence: referrer-policy missing

Acceptance
- Check text, layout and the main action “Get Started” at 1440×900 and 390×844.
- Preserve branding, authentication and business behavior. A screenshot does not prove broken interaction.
- Change only evidence-backed issues. Validate security headers against existing resources and authentication in report-only mode where supported.
- Compare before/after screenshots and run relevant functional tests. Do not claim untested behavior passed.A white composer floats over a blue-pink light field; a short headline and direct input establish the experience without technical jargon.
Black outlines, pink coins and a first-dollar promise make a commerce tool feel approachable to independent creators.
A collage of projects beneath minimal controls feels like an experimental design magazine opened onto the web.
A black canvas, purple download action and knowledge graph make a private thinking space visually tangible.