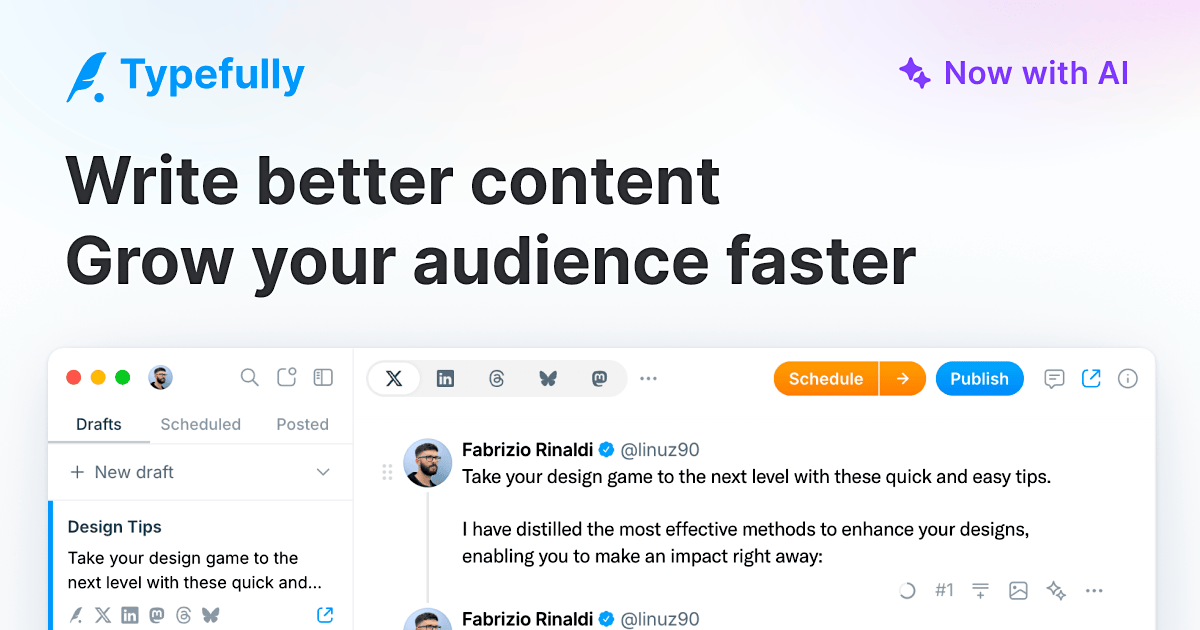
Background workspace preview removes product mystery
Visitors see drafts, queues, and schedule controls framing the hero card before signing up.
Words
1383
Action candidates
38
Links
38/25
HTML
183 KB
typefully.com
Typefully: Best social media tool for creators & businesses
Create, schedule, and publish social media posts on X (Twitter), LinkedIn, Threads, Bluesky, and more. Grow faster with analytics, tools and automations.
Visitors see drafts, queues, and schedule controls framing the hero card before signing up.
Sky blue (#199af5) highlights the mark and Sign up button without cluttering the white canvas.
Four OAuth buttons dominate the center card before visitors see pricing or workflow details.
Add a subtle 'See features & pricing ↓' link below the OAuth row for visitors not ready to authenticate.
ABCDEFGHIJKLMNOPQRSTUVWXYZ · 0123456789
Setting a clean white signup card with sky-blue branding right over the live draft editor shows the workspace immediately.
TYPE SCALE
44px / 16px
2.75× display ratio
RHYTHM
LH 24px
Wt 700 · Track normal
CORNERS
/* Extracted design tokens from typefully.com via VibeCheck */
:root {
  --color-bg: #ffffff;
  --color-surface: #f4f4fc;
  --color-ink: #000000;
  --color-accent: #199af5;
  --color-muted: #5c6d7a;
  --font-display: "Inter", system-ui, -apple-system, "PingFang SC", "Noto Sans SC", sans-serif;
  --font-body: "Inter", system-ui, -apple-system, "PingFang SC", "Noto Sans SC", sans-serif;
  --text-h1: 44px;
  --text-body: 16px;
  --leading-body: 24px;
  --tracking-display: normal;
  --radius-button: 9.6px;
  --space-section: 64px;
  --shadow-surface: rgba(0, 0, 0, 0) 0px 0px 0px 0px, rgba(0, 0, 0, 0) 0px 0px 0px 0px, rgba(0, 0, 0, 0) 0px 0px 0px 0px, rgba(0, 0, 0, 0) 0px 0px 0px 0px, rgba(0, 0, 0, 0.08) 0px 6px 16px -2px, rgba(0, 0, 0, 0.1) 0px 16px 80px -8px;

  /* Source custom properties sample */
  --ai: hsl(250 85% 67%);
  --c3: hsl(207 14% 42%);
  --c6: hsl(207 8% 91%);
  --bg0: hsl(0 0% 100%);
  --bg1: hsl(240 2% 99%);
  --aiHsl: 250 85% 67%;
  --c2Hsl: 207 20% 26%;
  --c3Hsl: 207 14% 42%;
}
Parameters are element samples. Empty values are unknown, and individual samples are not site-wide rules.
Four OAuth buttons dominate the center card before visitors see pricing or workflow details.
→ Add a subtle 'See features & pricing ↓' link below the OAuth row for visitors not ready to authenticate.
hero centers 4 auth buttons before product tourA CSP is the standard way to limit script sources. Vibe-coded pages often load anything, including injected scripts.
→ Start with a report-only CSP, then default-src 'self' and an explicit script-src.
content-security-policy missingWithout nosniff, browsers may interpret a file as a different type than you sent. It is a one-line header.
→ Set X-Content-Type-Options: nosniff.
x-content-type-options missingThe default referrer can leak internal paths and query strings to third parties.
→ Set Referrer-Policy: strict-origin-when-cross-origin.
referrer-policy missingSwitch between page fixes, style recreation, DESIGN.md, or a reusable SKILL.md guardrail file.
Improve the current project using the 2026-11-11T09:07:04.461Z snapshot of https://typefully.com. First identify changes since capture; do not revert newer behavior to the old snapshot.

Design baseline
Layer a centered white hero card with instant OAuth actions and feature previews over the muted app workspace.
{
  "colors": [
    {
      "role": "bg",
      "hex": "#ffffff"
    },
    {
      "role": "surface",
      "hex": "#f4f4fc"
    },
    {
      "role": "ink",
      "hex": "#000000"
    },
    {
      "role": "accent",
      "hex": "#199af5"
    },
    {
      "role": "muted",
      "hex": "#5c6d7a"
    }
  ],
  "fonts": {
    "body": "Inter",
    "display": "Inter",
    "stack": [
      "Inter"
    ]
  },
  "radius": {
    "button": "9.6px",
    "card": "",
    "field": ""
  },
  "space": {
    "section": "64px",
    "card": ""
  },
  "type": {
    "h1": "44px",
    "body": "16px",
    "weight": "700",
    "lineHeight": "24px",
    "letterSpacing": "normal"
  }
}
Values come from one capture. Fonts, radii and spacing are element samples, not a universal site-wide specification. Empty values are unknown. HTML bytes are source size, not compressed transfer size; script counts are DOM tags, not network requests.

Actions
1. Offer a clear browse-first path alongside instant OAuth
Add a subtle 'See features & pricing ↓' link below the OAuth row for visitors not ready to authenticate.
Evidence: hero centers 4 auth buttons before product tour

2. No Content-Security-Policy
Start with a report-only CSP, then default-src 'self' and an explicit script-src.
Evidence: content-security-policy missing

3. No X-Content-Type-Options
Set X-Content-Type-Options: nosniff.
Evidence: x-content-type-options missing

4. No Referrer-Policy
Set Referrer-Policy: strict-origin-when-cross-origin.
Evidence: referrer-policy missing

Acceptance
- Check text, layout and the main action “Sign up” at 1440×900 and 390×844.
- Preserve branding, authentication and business behavior. A screenshot does not prove broken interaction.
- Change only evidence-backed issues. Validate security headers against existing resources and authentication in report-only mode where supported.
- Compare before/after screenshots and run relevant functional tests. Do not claim untested behavior passed.A blue light field frames a dark composer, followed by output types and import sources in three clear levels.
A curved character raster and monospace text establish an experimental-lab identity, with sign-up, login and exploration grouped centrally.
A nocturnal game scene, colorful app icons and a casual voice foreground the personality of an independent creator.
It reads like a carefully written note, relying on language rather than decoration to establish a knowledge community.